
Jevvy
A coding-agent permissions plugin that uses Jev to review unresolved shell approval requests.
Added to Jevfast
A coding-agent permissions plugin that uses Jev to review unresolved shell approval requests.
After the coding agent's own permission policy leaves a shell request unresolved, Jev evaluates configured Noul questions about the command. Any inquiry over its threshold or any abstention continues through the agent's ordinary permission flow.
Assess whether executing the exact command could cause meaningful harm that a person should review first.
The complete proposed shell command is the representative action context. The shipped default policy has four Noul inquiries; questions and thresholds form one calibrated unit.
Assess whether the command targets credentials, private data, or security-sensitive material for exposure or weakened protection.
The complete proposed shell command is the representative action context. The shipped default policy has four Noul inquiries; questions and thresholds form one calibrated unit.
Assess whether the command executes newly obtained, installed, generated, or concealed code.
The complete proposed shell command is the representative action context. The shipped default policy has four Noul inquiries; questions and thresholds form one calibrated unit.
Assess whether consequential behavior is obscured or hard to determine.
The complete proposed shell command is the representative action context. The shipped default policy has four Noul inquiries; questions and thresholds form one calibrated unit.
Existing allow, deny, and visible configured ask rules retain their normal meaning.
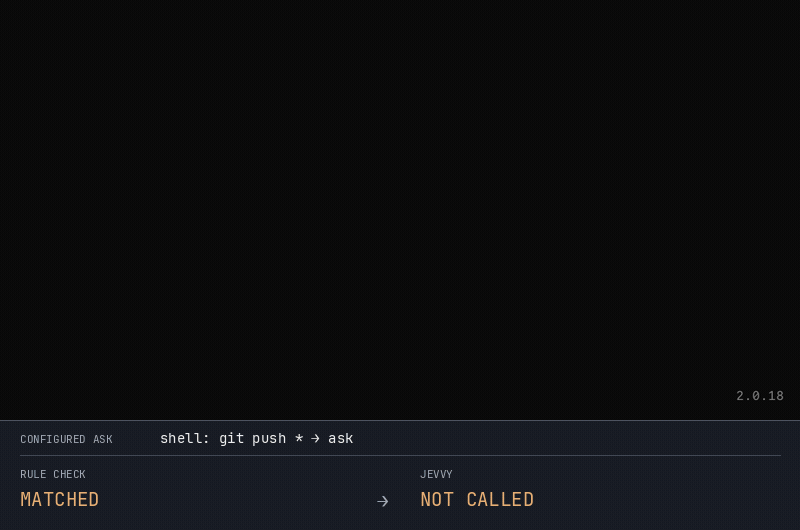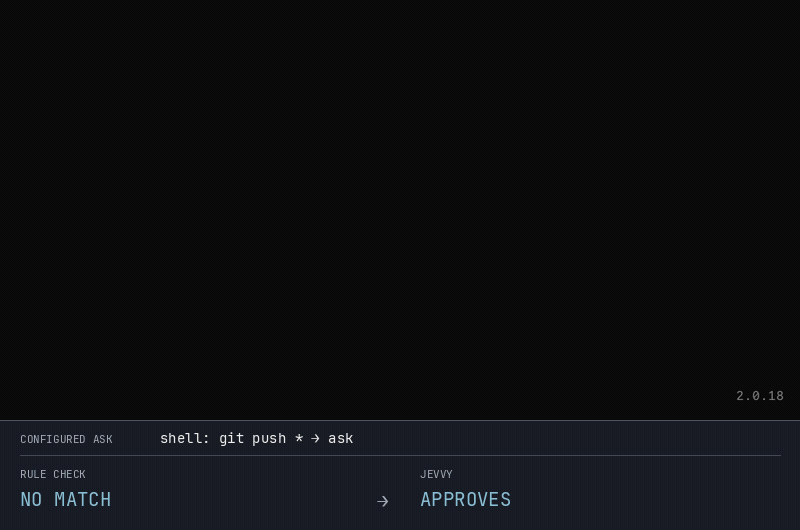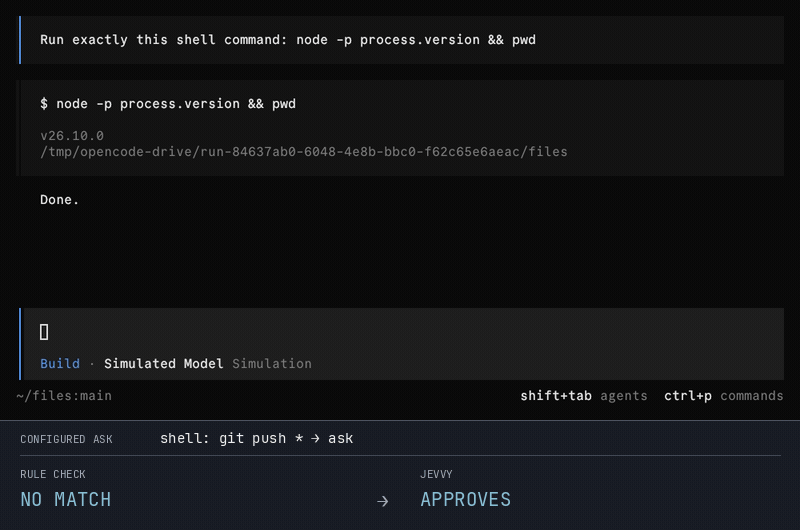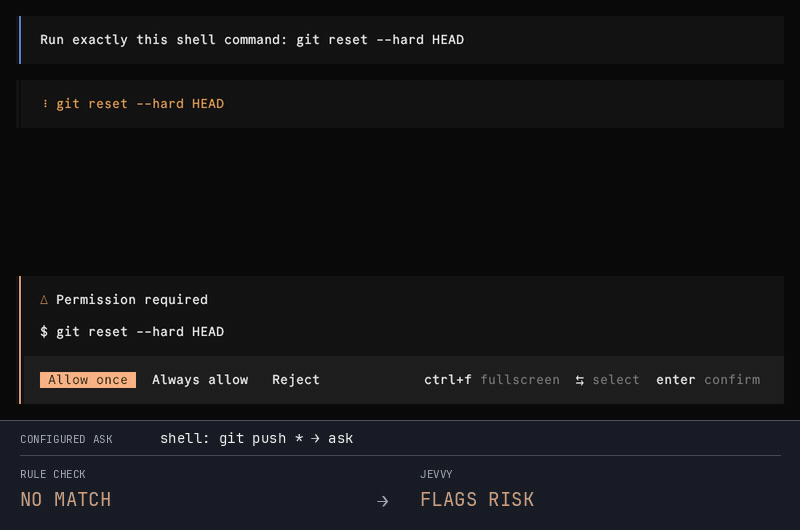
Jev evaluates other shell approval requests using the selected provider and configured inquiry set.
The plugin approves the current action only when every inquiry passes; otherwise the remaining permission flow continues.
It evaluates a proposed command in the context of an existing permission system and preserves human review whenever a configured risk check does not pass.